| Post Reply | RetroFed Forum Forum Index
» Programmer Humor
Page 1 of 3 Goto page 1, 2, 3 Next Last » |
| Author | Message | ||
|---|---|---|---|
 Ek-Hou-Van-Braai
piefed.social
Ek-Hou-Van-Braai@piefed.social Joined: 2025-05-14 |
|
||
| 1109 Original | |||
|
threeonefour
piefed.ca
threeonefour@piefed.ca Joined: 2025-06-07 |
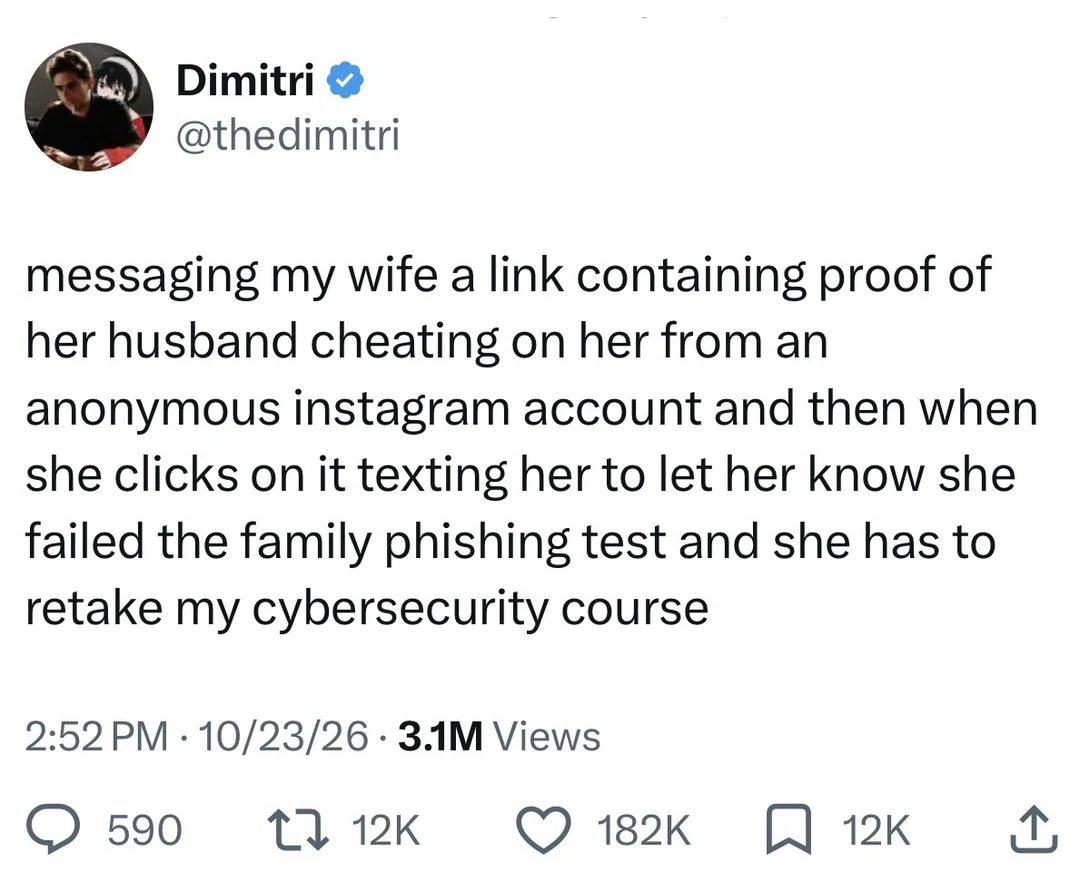
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them. |
||
| 172 | |||
 bizarroland
lemmy.world
bizarroland@lemmy.world Joined: 2023-06-08 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet. |
||
| 132 | |||
|
mindbleach
sh.itjust.works
mindbleach@sh.itjust.works Joined: 2023-08-27 |
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet.
|
||
| 40 | |||
|
SparroHawc
piefed.world
SparroHawc@piefed.world Joined: 2026-04-08 |
I failed one of those because I have script blockers on my browser and I wanted to see what the scam was. |
||
| 46 | |||
|
JelleWho
lemmy.world
JelleWho@lemmy.world Joined: 2024-10-20 |
I've set my last name in caps. So any IT Phishing script using a just sends my name in caps. And then I just set up a filter. They should really try and make them more believable |
||
| 27 | |||
|
P1nkman
lemmy.world
P1nkman@lemmy.world Joined: 2024-04-28 |
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet.
Be the change you want to see! I'll sign up straight away. |
||
| 21 | |||
|
Ignotum
lemmy.world
ignotum@lemmy.world Joined: 2023-06-12 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
I've also never fallen for any of the phising emails the IT department sends to test me, my secret is almost never checking my email |
||
| 38 | |||
|
ivan
piefed.social
ivan@piefed.social Joined: 2026-04-13 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
My place has this thing where most phishing test emails are obvious but every once in a while they’ll drop a really good one, sometimes these even pose as our managers. |
||
| 7 | |||
 neuracnu
lemmy.blahaj.zone
neuracnu@lemmy.blahaj.zone Joined: 2023-06-14 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
Kemming is 100 level preparedness. They need to up their game to cover internationalized homograph vulnerabilities, using roughly similar characters from different international alphabets to create totally different domain names: They look identical but are entirely different. |
||
| 21 | |||
|
balsoft
lemmy.ml
balsoft@lemmy.ml Joined: 2024-06-10 |
There's usually nothing wrong with just clicking a link (if your browser is set up correctly). The problem begins if you actually enter any sort of information in a random website or something. |
||
| 13 | |||
|
zerofk
lemmy.zip
zerofk@lemmy.zip Joined: 2025-06-04 |
There's usually nothing wrong with just clicking a link (if your browser is set up correctly). The problem begins if you actually enter any sort of information in a random website or something.
Be extra careful if you’re logged in on any other site in another tab though. Or even if you closed the tab. |
||
| 18 | |||
|
krashmo
lemmy.world
krashmo@lemmy.world Joined: 2023-07-03 |
I've also never fallen for any of the phising emails the IT department sends to test me, my secret is almost never checking my email
My company sends at least one fake phishing email a week. They track stats for them on a security page and I wear it as a badge of honor that my report says 100% viewed and 0% reported. |
||
| 17 | |||
|
gjoel
programming.dev
gjoel@programming.dev Joined: 2024-04-09 |
My place has this thing where most phishing test emails are obvious but every once in a while they’ll drop a really good one, sometimes these even pose as our managers.
The company I work for has lots of training to recognize phishing attempts, and then they proceed to send emails that tick most of the "avoid this" boxes. |
||
| 2 | |||
 FaceDeer
fedia.io
FaceDeer@fedia.io Joined: 2024-03-03 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
A company I was in a few jobs back had several layers of IT department, there was the local studio department that handled our everyday stuff and a "head office" somewhere far away that set policy and handed out budget and whatnot. One day "head office" IT decided it was a good idea to send out some fake phishing emails to "test" us. They didn't tell the local IT department about it, I guess they were also being "tested". My manager received one and only recognized it as a phishing attempt after he'd clicked just one too many things for it to feel safe to ignore. So he yanked the power on his computer and contacted the local IT department, as is protocol when something potentially dangerous just happened. The local network went into lockdown while local IT tried to figure out if something actually dangerous had happened. It cost the studio as a whole several hours of work time, which for a studio our size translated to an obscene dollar cost. Nobody on our side of things did anything wrong, even that one extra "dangerous" click my manager did wasn't something he could be blamed for - head office had crafted the fake phishing attempt well and his reaction to it would have prevented damage had it been real. Head office never tried a stunt like that again. |
||
| 54 | |||
 Catoblepas
lemmy.blahaj.zone
Catoblepas@lemmy.blahaj.zone Joined: 2023-06-13 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
Lmfao, .corn sounds like an instance someone would spin up to compete with lemmy.beans |
||
| 3 | |||
 urushitan 漆たん
kakera.kintsugi.moe
urushitan@kakera.kintsugi.moe Joined: 2026-03-28 |
ass.golf
Just leaving their bare ass out there with no ssl, smh |
||
| 34 | |||
|
Catoblepas
lemmy.blahaj.zone
Catoblepas@lemmy.blahaj.zone Joined: 2023-06-13 |
Be extra careful if you’re logged in on any other site in another tab though. Or even if you closed the tab.
Can you elaborate on this? |
||
| 3 | |||
|
TerHu
lemmy.dbzer0.com
TerHu@lemmy.dbzer0.com Joined: 2025-06-11 |
Can you elaborate on this?
from what i’ve heard, even if something isn’t able to break out of your browser, it may be able to gain access to cookies. those cookies in turn can carry a lot of info and even unlock some accounts. iirc that’s how the linux tech tips channel got into trouble. everyone, please correct me where i’m wrong. thank you. |
||
| 8 | |||
|
Ekky
sopuli.xyz
ekky@sopuli.xyz Joined: 2023-11-21 |
I failed one of those because I have script blockers on my browser and I wanted to see what the scam was.
Same, script blocker, virtual machine, etc. Found that apparently you are not meant to forward/report the scam to IT either. Moral of story: Never inform the company of any suspicious behavior; just ignore it. |
||
| 13 | |||
|
MummifiedClient5000
feddit.dk
MummifiedClient5000@feddit.dk Joined: 2023-06-09 |
I failed one of those because I have script blockers on my browser and I wanted to see what the scam was.
The URL is likely unique to identify you as soon as you have clicked. |
||
| 17 | |||
|
CrimeIsLegalNow
ani.social
CrimeIsLegalNow@ani.social Joined: 2026-09-09 |
Be the change you want to see! I'll sign up straight away.
P1nkman, please report to the training room. |
||
| 8 | |||
|
LastYearsIrritant
sopuli.xyz
LastYearsIrritant@sopuli.xyz Joined: 2025-02-20 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
If your company contracts with phish.me then that URL is actually in the email header metadata. Just set up a rule for the word phish to a special folder, and then you can use the "report" button on everything in that folder to get the credit. |
||
| 9 | |||
|
Catoblepas
lemmy.blahaj.zone
Catoblepas@lemmy.blahaj.zone Joined: 2023-06-13 |
from what i’ve heard, even if something isn’t able to break out of your browser, it may be able to gain access to cookies. those cookies in turn can carry a lot of info and even unlock some accounts. iirc that’s how the linux tech tips channel got into trouble. everyone, please correct me where i’m wrong. thank you.
Does that make it’s dangerous to log in persistently anywhere, period, in case you click on a shady link? I legitimately don’t know much and trust common sense prevention (run sites through virus total if I’m not familiar with them) and built in protection to do most of it, and I haven’t had any known password thefts from anything other than servers getting hacked. I do have an authenticator app and use it on really important stuff (government, school) but that’s about it. |
||
| 1 | |||
|
Geobloke
aussie.zone
Geobloke@aussie.zone Joined: 2025-06-30 |
This kills the trust |
||
| 9 | |||
|
LedgeDrop
lemmy.zip
LedgeDrop@lemmy.zip Joined: 2025-06-03 |
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet.
Oh, you mean like penisland.net? |
||
| 34 | |||
|
Ek-Hou-Van-Braai
piefed.social
Ek-Hou-Van-Braai@piefed.social Joined: 2025-05-14 |
Same, script blocker, virtual machine, etc. Found that apparently you are not meant to forward/report the scam to IT either. Moral of story: Never inform the company of any suspicious behavior; just ignore it.
There's a button that says report phishing for many companies |
||
| 9 | |||
 socsa
piefed.social
socsa@piefed.social Joined: 2024-08-20 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
I just take it one step farther and never open any email. If it's important you will CC my manager and he will physically come by my office and tell me about the email, giving me multi-factor phishing protection. If he demands I open an email then I am absolved of responsibility. |
||
| 7 | |||
|
balsoft
lemmy.ml
balsoft@lemmy.ml Joined: 2024-06-10 |
from what i’ve heard, even if something isn’t able to break out of your browser, it may be able to gain access to cookies. those cookies in turn can carry a lot of info and even unlock some accounts. iirc that’s how the linux tech tips channel got into trouble. everyone, please correct me where i’m wrong. thank you.
Cookies are specifically separated out per-domain. Your browser will not give a random website access to your auth cookies/localstorage for other websites. There are some awful companies which do set cross-website cookies (e.g. facebook, google, and other adware), but (1) those cookies are not auth credentials and are used mostly for fingerprinting and ad targeting, (2) should be filtered out by your browser's tracking protection (hence "if your browser is set up correctly"). Realistically there is still be a way for the website to fingerprint you enough to know who you are even without cookies, so the most adversarial outcome from clicking a link is that the attacker can know that you clicked that link, along with your general location (from geoIP) and some device info.
Nah, that was pretty much an .exe sent out by a fake sponsor, which was downloaded and executed. It then stole all browser data (including google auth cookies). Opening a link ≠ running an unsandboxed exe. |
||
| 10 | |||
|
bizarroland
lemmy.world
bizarroland@lemmy.world Joined: 2023-06-08 |
Oh, you mean like penisland.net?
Or girlsof in stagam, which apparently has disappeared but used to be the story of the adventures of a person called Girlsof in the magical realm of Stagram. |
||
| 17 | |||
|
balsoft
lemmy.ml
balsoft@lemmy.ml Joined: 2024-06-10 |
Be extra careful if you’re logged in on any other site in another tab though. Or even if you closed the tab.
No, you generally should not be worried about that. Generally the worst thing that a website can get from you just opening a URL is (1) whether or not you're logged in to google/facebook/etc, (2) your advertisement profile/who you are, (3) roughly where you are. All those are privacy issues, not a security issue, hence not very related to the "cybersecurity course", and only the first one is tangentially related to being logged in. You should of course use various anti-tracking measures, e.g. an adblocker, "resist fingerprinting" in Librewolf, user agent faker, a good VPN, etc. That will reduce the exposure to all 3 issues above, but once again those are not security problems. You should also never download random bullshit to your computer. Having an actual file on disk outside the browser sandbox could indeed be an issue. You could simply forget where it came from and decide to execute it one day, or there could be some bug in some app on your OS which could trigger a code execution exploit. However, if your browser shares authentication details with random websites like what you are describing, you should stop using it immediately. |
||
| 0 | |||
|
bisby
lemmy.world
bisby@lemmy.world Joined: 2023-06-21 |
If your company contracts with phish.me then that URL is actually in the email header metadata. Just set up a rule for the word phish to a special folder, and then you can use the "report" button on everything in that folder to get the credit.
KnowBe4 includes a bunch of headers in the email, including a disclosure saying they have permission to run the simulated phishing test. |
||
| 7 | |||
 Malica
lemmy.zip
Malica@lemmy.zip Joined: 2026-08-27 |
I saw one with a bunch of maga triggers. The Democrats are doing what!? 😱 they click every time. |
||
| 32 | |||
|
Ekky
sopuli.xyz
ekky@sopuli.xyz Joined: 2023-11-21 |
There's a button that says report phishing for many companies
Keyword here being "many companies". |
||
| 4 | |||
|
toynbee
lemmy.world
toynbee@lemmy.world Joined: 2023-08-02 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
Mine includes a header so their mark filter knows to ignore it. At this point, I'm pretty sure that every employee who has been there for more than a month has written or at least copied a filter to delete any email with that header. I've never been comfortable with that kind of mass deletion and we have, AFAIK, unlimited mailbox storage, so I just set my version to mark those emails as read. |
||
| 9 | |||
|
Saapas
piefed.zip
Saapas@piefed.zip Joined: 2025-11-23 |
This kills the trust
Yeah, the wife didn't trust the husband and clicked the link. Shameful, tbh |
||
| 6 | |||
|
TerHu
lemmy.dbzer0.com
TerHu@lemmy.dbzer0.com Joined: 2025-06-11 |
Cookies are specifically separated out per-domain. Your browser will not give a random website access to your auth cookies/localstorage for other websites. There are some awful companies which do set cross-website cookies (e.g. facebook, google, and other adware), but (1) those cookies are not auth credentials and are used mostly for fingerprinting and ad targeting, (2) should be filtered out b...
all i can say is that i need to log into outlook to log into teams, because logging into teams directly is broken, but the cross site cookie work… and reading stuff like adFection really doesn’t instill confidence in opening random websites. but most probably you’re right for most cases. |
||
| 2 | |||
|
TerHu
lemmy.dbzer0.com
TerHu@lemmy.dbzer0.com Joined: 2025-06-11 |
Does that make it’s dangerous to log in persistently anywhere, period, in case you click on a shady link? I legitimately don’t know much and trust common sense prevention (run sites through virus total if I’m not familiar with them) and built in protection to do most of it, and I haven’t had any known password thefts from anything other than servers getting hacked. I do have an authenticator ap...
well, i’ve been taught that keeping cookies around is somewhat dangerous, and that because of that browsers like librewolf always clear your cookies. i’m by no means an expert tho, so you might wanna read the other commenters input on that. |
||
| 1 | |||
|
criticon
lemmy.ca
criticon@lemmy.ca Joined: 2023-07-06 |
My company sends at least one fake phishing email a week. They track stats for them on a security page and I wear it as a badge of honor that my report says 100% viewed and 0% reported.
My company makes you take a course of you fail one or if you ignore 4 or 5 so I have the highest reporting record of the company just because of how much I hate that course |
||
| 9 | |||
|
balsoft
lemmy.ml
balsoft@lemmy.ml Joined: 2024-06-10 |
all i can say is that i need to log into outlook to log into teams, because logging into teams directly is broken, but the cross site cookie work… and reading stuff like adFection really doesn’t instill confidence in opening random websites. but most probably you’re right for most cases.
Thankfully I don't even have an MS account, but I do implore you to check out the cookies and see for yourself that they will have a specific list of domains they are valid for. Open the browser developer menu on an Outlook tab (F12), navigate to "Storage" → "Cookies" (may be named slightly differently in different browsers), and look at the "Domain" column in the table.
The problem there is website operators selling their adspace to a literal israeli spyware company, which meant injecting adversarial javascript into their own pages. It was not a case of "user opening a random link", rather it was the website operator themselves forwarding the user malicious JS from the "ad company". As a user there's generally nothing you can do to prevent this kind of attack where the website itself was compromised; besides, without another vulnerability/attack vector the impact will be limited to the website in question. |
||
| 2 | |||
 Psaldorn
lemmy.world
Psaldorn@lemmy.world Joined: 2023-06-30 |
Unexpected YouTube drama reference |
||
| 1 | |||
|
krashmo
lemmy.world
krashmo@lemmy.world Joined: 2023-07-03 |
My company makes you take a course of you fail one or if you ignore 4 or 5 so I have the highest reporting record of the company just because of how much I hate that course
I think they do that at my company too but in addition to not reporting phishing emails I have a personal rule that I don't do any "mandatory" training unless someone in my management chain specifically asks me to. My boss probably gets annoyed by that occasionally but you'd be surprised how much of that stuff I never get asked about. |
||
| 9 | |||
|
trxxruraxvr
lemmy.world
trxxruraxvr@lemmy.world Joined: 2023-06-19 |
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet.
This reminded me of notpron.com |
||
| 6 | |||
|
P1nkman
lemmy.world
P1nkman@lemmy.world Joined: 2024-04-28 |
P1nkman, please report to the training room.
But there's nothing here 😭 |
||
| 6 | |||
|
AHorseWithNoNeigh
piefed.social
AHorseWithNoNeigh@piefed.social Joined: 2025-09-04 |
Just leaving their bare ass out there with no ssl, smh
 It's only one ssl. How much could it possibly cost? 4 dollars?! |
||
| 13 | |||
|
mindbleach
sh.itjust.works
mindbleach@sh.itjust.works Joined: 2023-08-27 |
Just leaving their bare ass out there with no ssl, smh
I tried securing my ass, but my browser got stuck. |
||
| 4 | |||
|
wal_kr
lemmy.world
wal_kr@lemmy.world Joined: 2023-06-30 |
Or girlsof in stagam, which apparently has disappeared but used to be the story of the adventures of a person called Girlsof in the magical realm of Stagram.
I remember that one too, but think it was actually called Slütsof In Stagrâm |
||
| 14 | |||
 TrickDacy
lemmy.world
TrickDacy@lemmy.world Joined: 2023-07-27 |
There's usually nothing wrong with just clicking a link (if your browser is set up correctly). The problem begins if you actually enter any sort of information in a random website or something.
This is extremely bad advice and is akin to saying there is nothing wrong with shooting someone in the chest as long as they're wearing a bulletproof vest. Sketchy websites should be avoided. Even experts don't think of everything possible to attack. It's the same reason you shouldn't expose your pc directly to the internet even if you have a secure os installed. ...Bonus points for you in another thread today doubting that it's possible to lock one's keys in a car. |
||
| 11 | |||
|
hypnicjerk
piefed.social
hypnicjerk@piefed.social Joined: 2025-12-01 |
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
lucky you. they fail us if we don't right click report phishing. |
||
| 8 | |||
|
marduk
lemmy.today
marduk@lemmy.today Joined: 2023-11-24 |
It's only one ssl. How much could it possibly cost? 4 dollars?!
I the worst part is deciding which flavor to get
|
||
| 13 | |||
|
trxxruraxvr
lemmy.world
trxxruraxvr@lemmy.world Joined: 2023-06-19 |
all i can say is that i need to log into outlook to log into teams, because logging into teams directly is broken, but the cross site cookie work… and reading stuff like adFection really doesn’t instill confidence in opening random websites. but most probably you’re right for most cases.
This works because loggin in to outlook sets a cookie for login.microsoftonline.com which is reused by other Microsoft products. Each product requests a token from login.microsoftonline.com and as long as you have a valid cookie for that domain it will return a token that the app (outlook/teams/onedrive/etc) can use to access its own api. The cookie itself stays bound to login.microsoftonline.com and it's never shared with other domains and the service at login.microsoftonline.com will not provide tokens to requests from non-microsoft domains. |
||
| 6 | |||


| Post Reply |
Page 1 of 3
Goto page
1, 2, 3
Next
Last »
Back to top |