| Post Reply | RetroFed Forum Forum Index » Privacy |
| Author | Message | ||
|---|---|---|---|
|
technocrit
lemmy.dbzer0.com
technocrit@lemmy.dbzer0.com Joined: 2024-02-19 |
|
||
| 88 Original | |||
|
Mark with a Z
suppo.fi
markz@suppo.fi Joined: 2025-07-04 |
Don't tell me people are using llms to generate passwords |
||
| 73 | |||
 Kogasa
programming.dev
kogasa@programming.dev Joined: 2023-06-12 |
Don't tell me people are using llms to generate passwords
People are using LLMs to diagnose disease, write prescriptions, deny health care claims, deny loans and grants, write scientific papers, review scientific papers, draft engineering and architectural documents, and talk to their loved ones Despair |
||
| 52 | |||
 Steve
communick.news
Steve@communick.news Joined: 2023-08-05 |
Don't tell me people are using llms to generate passwords
Very well. If you don't want me to tell you the truth about people using LLMs to make passwords, I won't. |
||
| 13 | |||
 KazuyaDarklight
lemmy.world
KazuyaDarklight@lemmy.world Joined: 2023-06-12 |
Don't tell me people are using llms to generate passwords
Getting away from more direct requests I can absolutely imagine AI offering passwords/suggestions as part of a coding session. Including "temp" passwords that look secure so "why bother changing it?". |
||
| 5 | |||
|
mr_anny
sopuli.xyz
mr_anny@sopuli.xyz Joined: 2026-02-08 |
Not again this horrible web design/engine whatever laggin/stuttering the way it almost induce a epileptic seizure in me. |
||
| 4 | |||
|
Phoenixz
lemmy.ca
phoenixz@lemmy.ca Joined: 2023-06-10 |
This is akin to asking Karen from accounting to generate a password for you, and trusting that it will be a true random and secure password and that she won't yap about it to everyone. That statement is one of the painfully dumbest things I've read in my life, and I've read the bible. |
||
| 13 | |||
 Melobol
lemmy.ml
Melobol@lemmy.ml Joined: 2023-06-24 |
Why not do this.... |
||
| 15 | |||
 64bithero
lemmy.world
64bithero@lemmy.world Joined: 2026-01-27 |
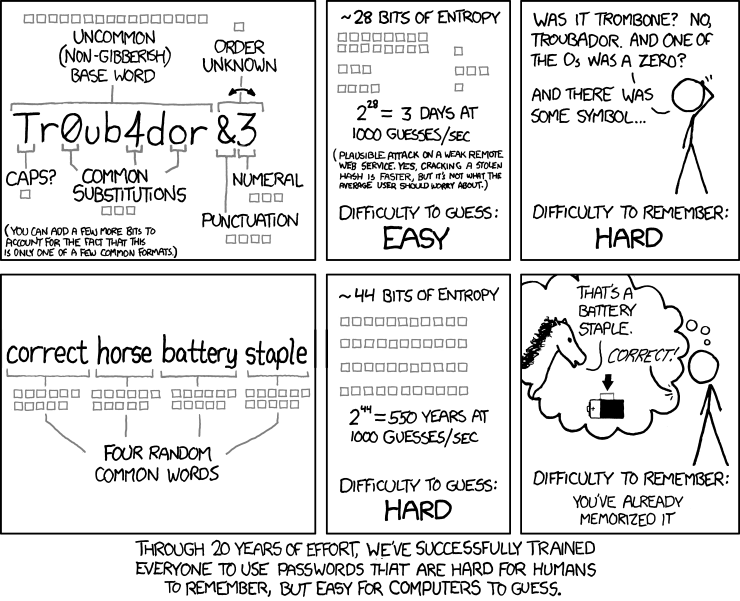
Why not do this.... Corect horse battery staple
Yes! QuiltedNematoadNotepad486 |
||
| 2 | |||
|
Ephera
lemmy.ml
Ephera@lemmy.ml Joined: 2020-05-31 |
Don't tell me people are using llms to generate passwords
I imagine, it's a matter of asking it to generate some configuration and one of the fields in that configuration is for a password, so the LLM just auto-completes what a password is most likely to look like. |
||
| 3 | |||
|
64bithero
lemmy.world
64bithero@lemmy.world Joined: 2026-01-27 |
Irregular ? Like my bowel movements ? |
||
| 4 | |||
 Eager Eagle
lemmy.world
eager_eagle@lemmy.world Joined: 2023-07-07 |
Why not do this.... Corect horse battery staple
pls don't spread my password around like that |
||
| 4 | |||
|
Ephera
lemmy.ml
Ephera@lemmy.ml Joined: 2020-05-31 |
Why not do this.... Corect horse battery staple
The problem is that in this case, the LLM just naively auto-completes a password from what it knows a password to most likely look like. It is possible to enable an LLM to call external tools and to provide it with instructions, so that it's likely to auto-complete the tool call instead. Then you could have it call a tool to generate a correct horse battery staple, or a completely random password by e.g. calling the But yeah, that just isn't what this article is about. It's specifically about cases where an LLM is used without tool calls and therefore naively auto-completes the most likely password-like string. |
||
| 8 | |||
|
trailee
sh.itjust.works
trailee@sh.itjust.works Joined: 2024-02-25 |
Why not do this.... Corect horse battery staple
Many password manager generators already do (use the "memorable" type). |
||
| 11 | |||
|
Melobol
lemmy.ml
Melobol@lemmy.ml Joined: 2023-06-24 |
The problem is that in this case, the LLM just naively auto-completes a password from what it knows a password to most likely look like. It is possible to enable an LLM to call external tools and to provide it with instructions, so that it's likely to auto-complete the tool call instead. Then you could have it call a tool to generate a correct horse battery staple, or a completely random passwo...
I'm kinda interested how nany accounts you could log in with those strings :D |
||
| 3 | |||
|
guy
piefed.social
guy@piefed.social Joined: 2024-11-20 |
Welp, that's another thing I hadn't thought you could use llms for and another thing I would never do |
||
| 25 | |||
 chicken
lemmy.dbzer0.com
chicken@lemmy.dbzer0.com Joined: 2023-06-30 |
Don't tell me people are using llms to generate passwords
Even where they aren't, I bet this is something that could end up happening when using them as open-ended agents that might try making their own accounts. The article also mentions this:
|
||
| 4 | |||
 fiatcode
lemmy.ml
fiatcode@lemmy.ml Joined: 2026-03-30 |
Don't tell me people are using llms to generate passwords
I know someone who generate passwords in AI chat |
||
| 0 | |||

| Post Reply |
Back to top |